Why line count is a broken proxy for pull request risk
Traditional engineering metrics measure pull request size by lines added and deleted. In practice, production outages often trace back to small, subtle modifications to connection pools, retry loops, authentication guards, or schema migrations.
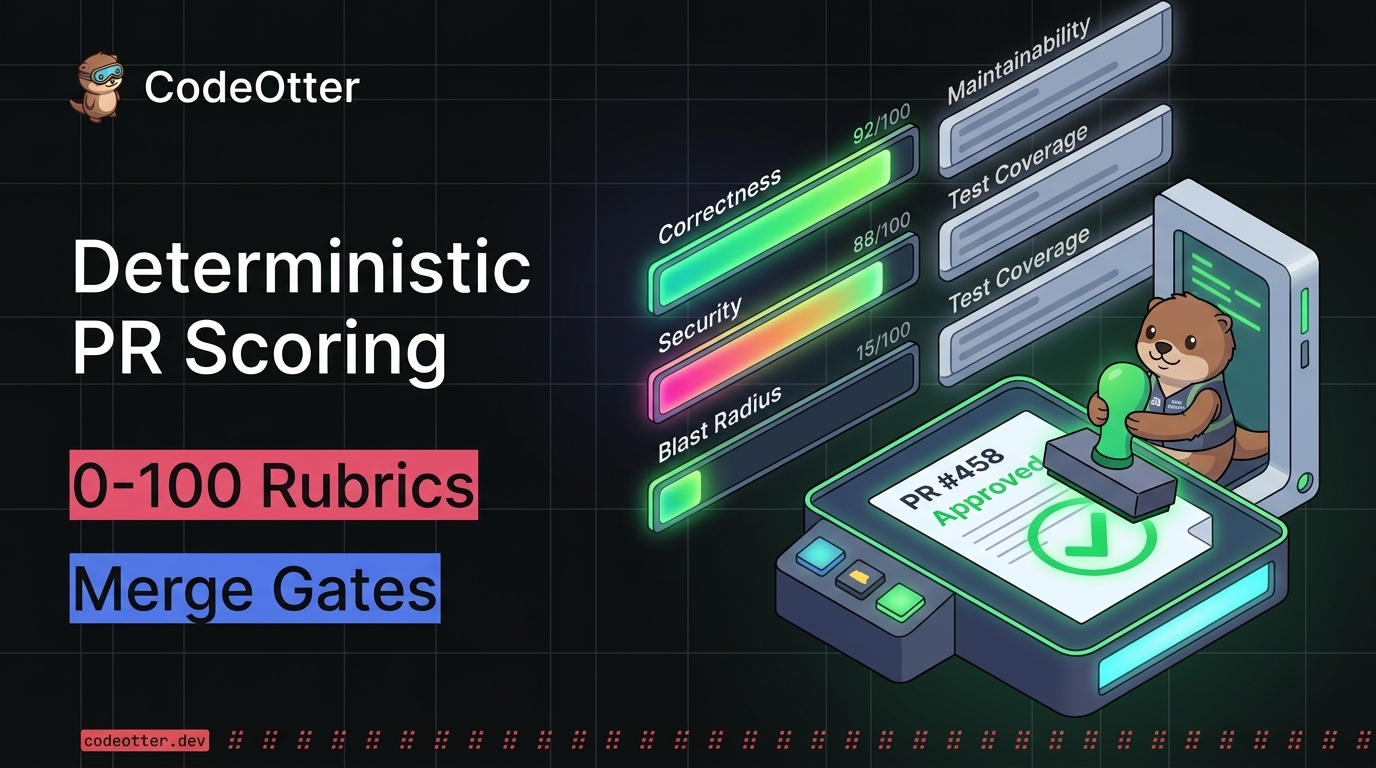
CodeOtter evaluates Blast Radius as an explicit System One gauge alongside Quality, Risk, Tests, Readability, and PR Hygiene—rating how far a change reaches, up to system-wide or critical-path impact (auth, payments, migrations, deploy).
A binary Security gate alongside the Risk score
Alongside the 0–100 Risk score, CodeOtter's System One model answers a binary Security gate from S1_GATES: a yes/no question asking whether the change introduces a security risk (injection, auth bypass, secrets, unsafe deserialisation, SSRF, XSS). A yes fails the gate: it shows as a Warning row in the pull request comment, and codeotter ci exits with code 1 when any gate fails, so a pipeline can stop on it. Those concerns are therefore a pass/fail check rather than a score.