Enterprise AI code reviews on Azure Repos
For engineering organizations building inside Microsoft Azure, security, compliance, and deep pipeline integration are top priorities. Development teams rely on Azure DevOps to coordinate complex enterprise architectures, but reviewing high-velocity pull requests remains a critical bottleneck.
With CodeOtter v0.4.0, we are thrilled to release native integration for Azure DevOps.
Now, teams can deploy CodeOtter within their private Azure virtual networks, connect directly to Azure Repos, and run dual-engine AI code reviews without compromising data sovereignty.
What is included in the Azure DevOps integration
1. Azure DevOps OAuth & Organization Mapping
Connect smoothly with Azure DevOps organizations and projects:
- Enterprise Single Sign-On (SSO) backed by Microsoft Entra ID (formerly Azure Active Directory).
- Project-level scoping to ensure review bot permissions adhere to your organization's security posture.
- Support for both cloud-hosted Azure DevOps Services and hybrid self-hosted configurations.
2. Native Azure Repos Pull Request Integration
CodeOtter interacts with the Azure DevOps Git REST API to provide seamless pull request experiences:
- Interactive Discussion Threads: Review suggestions are posted as native Azure Repos pull request discussion threads, allowing engineers to accept, edit, or resolve recommendations inline.
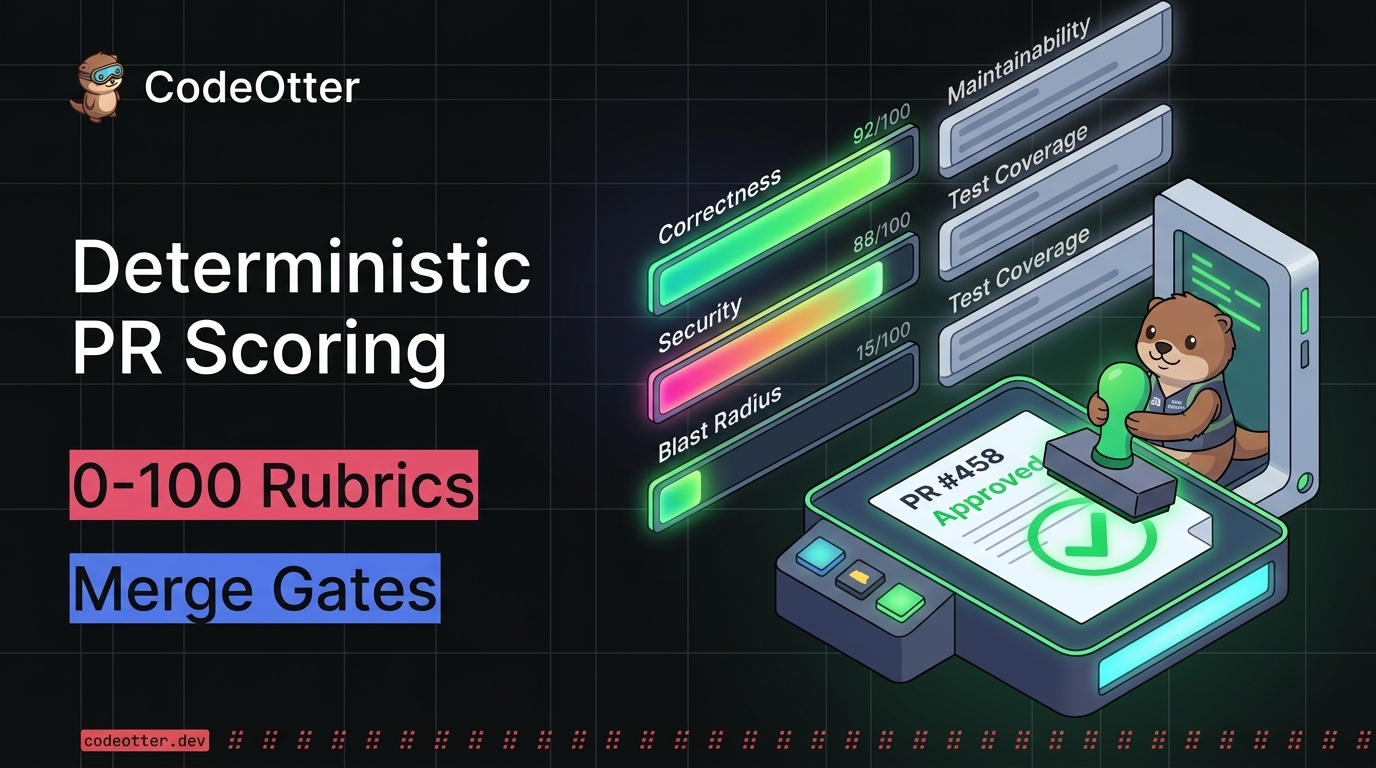
- Comprehensive Scorecards: A dedicated review summary comment provides immediate visibility into code quality, test adequacy, and blast radius.
- Thread Status Management: Automatically marks comment threads as active or closed when addressing commits are detected.
3. Enterprise Blast-Radius & Security Gates
Enterprise codebases often feature interconnected microservices where a change to a shared library can ripple across multiple downstream systems. CodeOtter enforces strict binary gates on Azure Repos:
- Blast Radius Analysis: Flags high-risk changes that touch public API contracts, shared schemas, or infrastructure definitions.
- Pre-Merge Safety Gates: 9 binary gates verifying security patterns, architectural compliance, documentation updates, and test coverage before PR completion.
- Branch Policy Integration: Tie CodeOtter gate results into Azure DevOps required status checks and branch policies.
4. Zero-Egress Cloud & Hybrid Privacy
Because CodeOtter is fully self-hosted, enterprise teams can keep all code analysis strictly within their Azure tenant:
- Deploy CodeOtter in Azure Container Apps or Azure Kubernetes Service (AKS).
- Use Azure OpenAI Service endpoints or local offline GGUF sidecars for complete compliance and zero third-party data egress.
Universal Dual-Engine Review Architecture
Every Azure Repos pull request triggers CodeOtter's dual-engine analysis pipeline:
- System One Rubric & Gate Engine: Runs typed deterministic checks to generate 0–100 quality gauges and enforce 9 binary pre-merge gates.
- Generative Language Model Engine: Produces file-by-file walkthroughs, executive summaries, and line-level refactoring diffs.
All results pass through our judge() normalization system before reaching Azure Repos, guaranteeing reproducible and auditable code reviews.
Get Started with Azure DevOps
Connecting Azure DevOps to CodeOtter takes just a few steps:
- Register an application in Azure DevOps or create a scoped Personal Access Token / OAuth app.
- Provide your Azure DevOps Organization URL and credentials in the CodeOtter admin settings.
- Select your Azure Repos projects to activate automated PR reviews.
- Release Downloads: GitHub Release v0.4.0
- Documentation: Explore our Azure DevOps deployment and branch policy setup guides.